A debt collector finishes a call and records that the consumer does not want another call. Meanwhile, an email sequence is queued for the afternoon and a letter vendor has already received tomorrow’s file. This is where cease and desist debt collection becomes an operational problem rather than a question of whether an individual debt collector heard the request. A restriction must reach every workflow that could act on the account, with the scope of the consumer’s request preserved.
Capture the Scope of Each Cease Request
The first job is to preserve what the consumer actually said. “Do not call my mobile number” is different from “stop contacting me about this debt.” A text reply of STOP normally concerns that messaging channel; a broad written cease-communication request under the Fair Debt Collection Practices Act (FDCPA) may have wider consequences. Capture the original wording, receipt date, channel, associated number or address, consumer identity, and the employee or system that received it. Do not reduce every phrase to an undifferentiated opt-out flag.
For a mailed cease and desist letter, keep the correspondence and delivery details, including certified mail information when available. A consumer may refer to the original creditor, ask to dispute the debt, or send a dispute letter at the same time. Preserve those requests separately. The intake queue should let collectors recognize uncertainty without interpreting legal rights on the fly.
For third-party debt collectors, recording a cease and desist letter is different from confirming that its restrictions are active. A consumer may also use the phrase debt validation letter when requesting information after a validation notice. Keep that request distinct from a communication restriction. Supervisors should see what awaits review, which account is blocked, and why, without relying on collectors to improvise a workaround. Each debt collector should see the resulting restriction immediately.
Capture channel preferences in the same record used by digital communication controls, so the request's wording, scope, and receipt time remain available when the next action is evaluated.
Suppress Calls, Texts, Emails, and Letter Batches
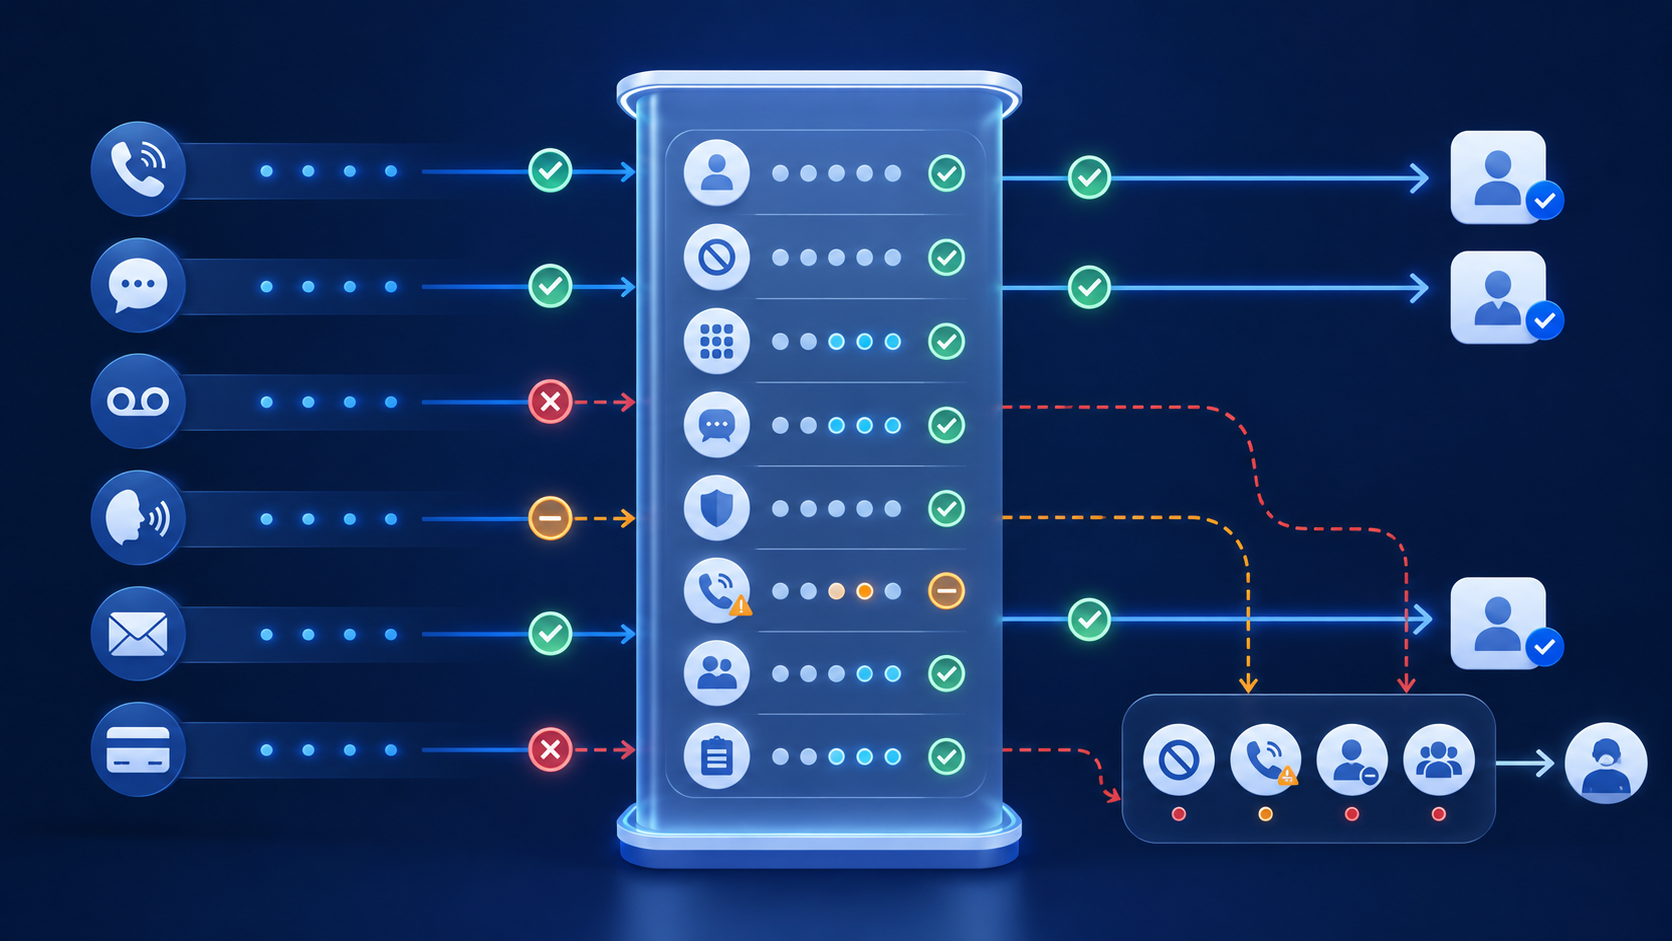
An account restriction should affect dialers, SMS campaigns, email sequences, voicemail drops, and letter batches according to its scope. Check both live queues and work already exported to vendors. If the agency sends a nightly file, the suppression mechanism needs a way to catch changes that arrive after that export. The system should recheck permission immediately before each action rather than trusting the permission state when the sequence was created.
Do not treat an account note as adequate enforcement. If the debt collector sees a flag but an external dialer does not, collection calls may continue. If a consumer opts out of email only, the team should not automatically assume every form of contact is forbidden. Record the applicable restriction, propagate it through integrations, and require review before anyone overrides it.
This is where reliable systems matter more than an attractive dashboard. An action in one channel can change what should happen in another. A transaction, restriction, dispute, assignment, or client instruction needs to reach the relevant tools before those tools act again. Connected workflows also make troubleshooting easier: when something fails, an operator can see the failed step and the last confirmed state instead of searching disconnected vendor logs.
Effective omnichannel outreach controls must reach vendor queues as well as collector screens; cancelling tomorrow's email matters just as much as displaying today's account restriction.
Review Permitted Notices and Preserve Cease-Request Evidence
The FDCPA and Regulation F distinguish a broad written cease and desist letter from other requests and recognize limited exceptions. Under federal law, 15 U.S.C. § 1692c(c) addresses ceasing communication. Exceptions are not permission to restart routine collection efforts. Route uncommon notices through compliance review and counsel. Filing a lawsuit, the statute of limitations, time-barred debt, and credit reporting to credit bureaus require separate analysis; a cease request never means automatic debt resolution.
Retain the policy version, reviewed decision, date, communication history, and account state that explains what happened. If debt buyers or an original creditor later ask about activity, an auditable record is stronger than a collector’s recollection. The same applies if a Consumer Financial Protection Bureau complaint or internal audit requires the agency to reconstruct events.
For leadership, the question is whether the debt collection agency can catch a delayed vendor event, conflicting rule, or missing approval before it affects a consumer. Ask counsel how failures may expose the agency to statutory damages or attorney's fees. Give exception rates and resolution times the same attention as completed work; speed should not conceal a growing review backlog.
Build cease-request audit trails around the received instruction, applied restriction, reviewer, and subsequent events so an investigator can reconstruct the decision without relying on memory.
Test Cease-Request Suppression Across Vendors
For third-party debt collectors, appoint one process owner accountable across collections, compliance, finance, technology, and client services. The owner should define the specific trigger, the minimum reliable account data, the permitted automated actions, and the conditions that require a human decision. This prevents an important control from becoming everybody's responsibility and nobody's task.
Test a cease request at several points in the outreach cycle: before a dialer list is built, after an SMS is scheduled, and after a letter file reaches a mailing vendor. Confirm that the restriction reaches each destination before another contact attempt occurs. Record the time of the request, the time each channel was suppressed, and any queue that required manual intervention. That timeline is your strongest evidence of execution.
Confirm Override Authority and Exception-Notice Controls
Have counsel distinguish FDCPA cease requests from channel-specific preferences before changing workflows. Review CFPB Regulation F and Federal Trade Commission (FTC) guidance when approving exception notices. Document who receives vendor suppression failures, who can authorize permitted communication, and which evidence supports that decision. Use CFPB complaint reviews to check whether the preserved request, restriction, and action history tell the same story.
Ask vendors to demonstrate a cease request stopping queued outreach. Check who can approve any communication that remains permitted and where the decision is recorded.
For cease requests, we offer connected account records and configurable communication workflows that agencies can evaluate for coordinating channel restrictions, managing exceptions, and retaining a clear history of what happened after a consumer asked for contact to stop.
Final Thoughts: Make Cease Requests Operational
A cease request isn't resolved when someone adds a note to the account. It's resolved when the appropriate restriction reaches the dialer, messaging sequences, letter vendor, and any other system that could initiate contact. That requires a clear record of what the consumer requested, a way to catch work already queued, and a controlled review process for communications that may still be permitted. In cease and desist debt collection, the quality of that handoff matters more than how quickly a collector closes the task.
In an Aktos demonstration, bring a real suppression scenario and ask to trace the request from intake through each affected communication channel.
FAQs
Q: Does a text opt-out stop phone calls?
A: Not automatically. A text-message opt-out generally signals a restriction on that channel, while a broader cease-communication request may have different legal consequences. Record the exact language and obtain compliance review when unclear.
Q: How should agencies document cease-communication requests?
A: Keep the original request, timestamp, channel, account identifier, applied restrictions, affected vendor systems, review decisions, and any later authorized changes.