Healthcare Debt Collection Software Guide
HIPAA is essential in healthcare collections, but it is not the whole software evaluation. Secure software can still fail operationally when placements lack patient, guarantor, service, insurance, document, or client-rule context.
That is why healthcare debt collection software should be evaluated as a data and workflow system, not just a compliance checkbox. It needs to protect sensitive information while preserving the context required for account resolution, payment plans, disputes, client reporting, and revenue recovery. Those same operational considerations are central to building HIPAA-compliant AI for medical collections.
Healthcare Collection Data Is More Complex Than a Balance
A healthcare placement may move from a provider’s revenue cycle management (RCM) environment to a third-party agency after earlier billing activity. A balance alone is rarely enough. Collectors may need patient, guarantor, insurance, and document context, while client leaders track DSO, write-offs, recovery rates, and placement performance. Modern debt collection software should preserve that context without manual reconstruction.
Start With Accurate Patient and Guarantor Information
The placement should clearly distinguish the patient from the guarantor when they are not the same person. It should also include reliable contact information, relationship data, account identifiers, and other fields the agency has been authorized to receive and use.
Accuracy matters because patient communication, payment processing, disputes, and reporting depend on the correct identity and account relationship. Poor mapping can create duplicate accounts, incorrect outreach, or extra research. Agencies should define the identifiers required to match records across the collection platform and client EHR.
Preserve Service-Level Context
Healthcare debt often needs service context that other portfolios may not. Useful placement data can include date of service, provider, facility, service or account identifiers, and the balance components the creditor has approved for collection.
This does not mean every collector should see every clinical detail. In fact, access should be limited to what is necessary for the work. HHS explains that the HIPAA Privacy Rule establishes standards for protecting protected health information, while its minimum-necessary guidance emphasizes limiting unnecessary access and disclosure.
For agencies, that makes the data model and permissions just as important as the number of fields available.
Bring Insurance Context Into the Placement
Collectors should not have to guess whether a balance reflects patient responsibility after insurance activity. Where appropriate and authorized, the placement may need relevant payer status, amounts applied, remaining patient responsibility, and enough context to explain why the account reached collections.
The purpose is operational clarity, not recreating the entire EHR. Missing insurance context can force staff to send questions back to the client, delaying account resolution and weakening the consumer experience.
Transfer Supporting Documents With the Account
Statements, notices, account records, relevant correspondence, and verification documentation should be available through a controlled document workflow. If files live in a separate portal or must be requested manually, disputes and client questions take longer to resolve.
Documents should remain linked to the account, with audit trails showing when they were added, viewed, replaced, or sent. That matters when an agency must substantiate the debt or respond to a dispute.
For covered debt collectors, the FDCPA and the CFPB’s current Regulation F remain core federal frameworks. Agencies should work with qualified counsel on how those rules, TCPA requirements, state law, client policy, and healthcare-specific obligations apply to their workflows.
Capture Client-Specific Rules
Healthcare clients may differ on settlement authority, payment plans, escalation rules, communication requirements, return criteria, and approval thresholds. Those rules should live in the workflow rather than inside documents that collectors have to remember.
One client may allow certain payment plans or an online payment through self-service portals without approval; another may require supervisor review. Configurable rules help collection agency software support multiple clients without turning every placement into a manual process.
Preserve Communication Preferences and Consent Context
A complete placement should include known language preferences, channel restrictions, relevant consent information, and communication preferences the creditor is authorized to pass to the agency.
That context can guide omnichannel communication across calls, SMS, email, letters, IVR, and portals. Payment reminders should reflect the current account status. The goal is coordinated patient communication in which every channel respects the same account state and approved rules.
Apply Role-Based Data Access
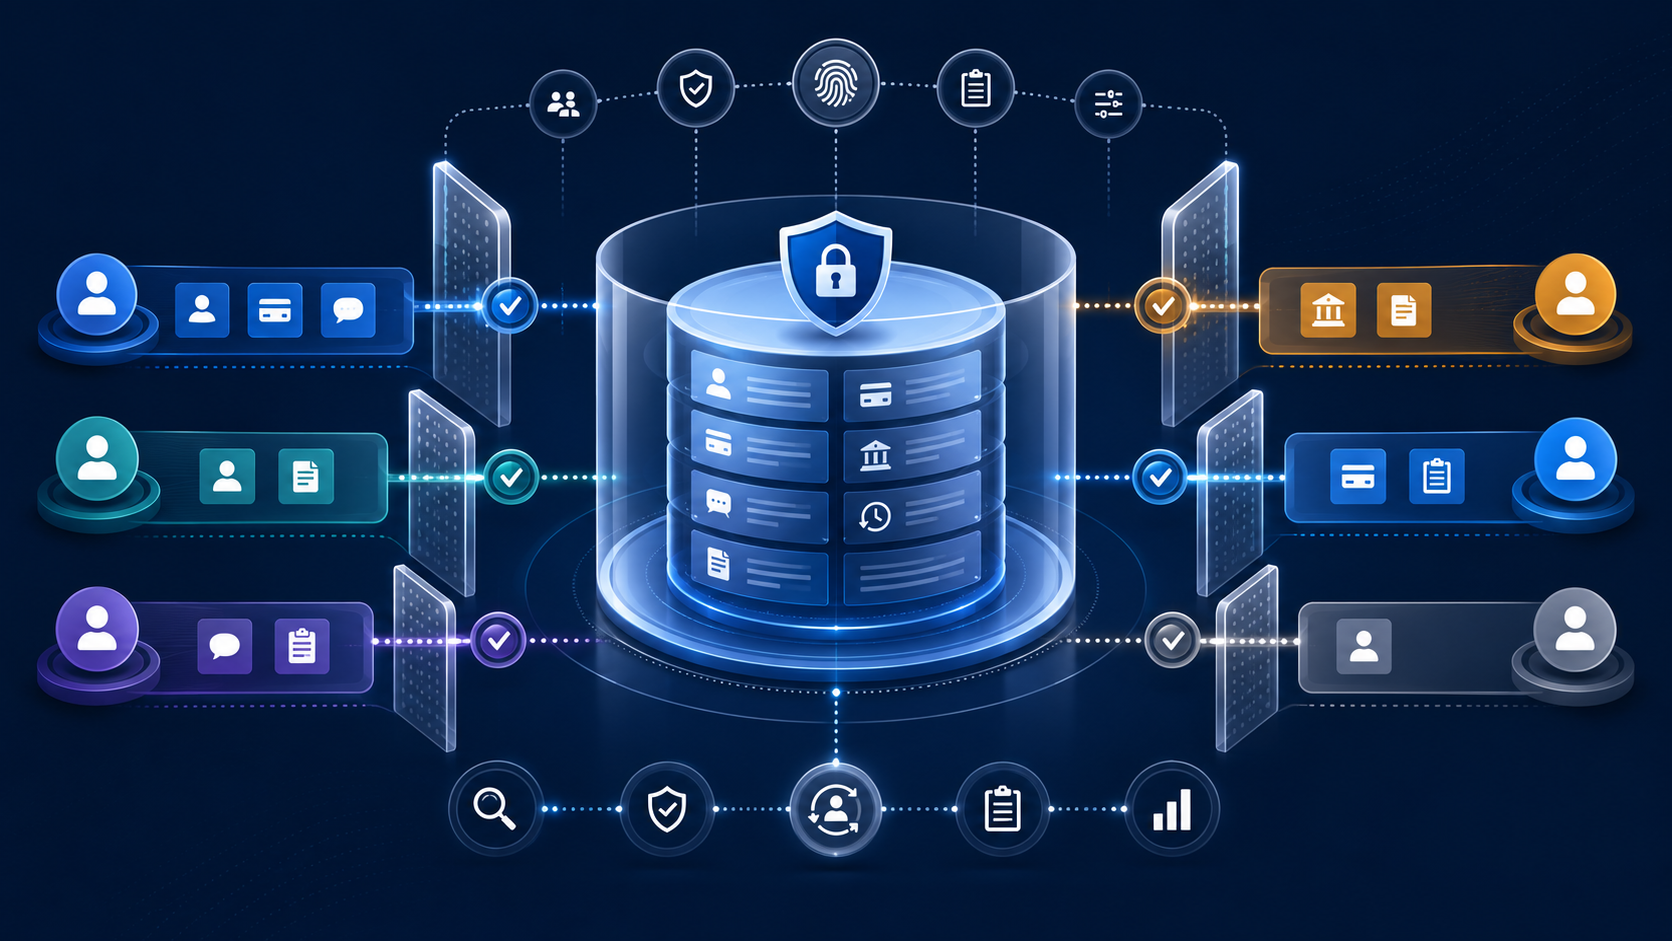
Healthcare collections make role-based access control especially important. A collector, supervisor, compliance analyst, client-services user, and administrator may need different capabilities.
The HHS HIPAA Security Rule requires administrative, physical, and technical safeguards for electronic protected health information. In software terms, agencies should evaluate data security controls such as authentication, permissions, logging, secure transmission, and access review based on their responsibilities and risk environment.
Strong access controls for collection agencies help ensure sensitive collection data is only available to the people who actually need it.
Synchronize Agency and Healthcare Systems
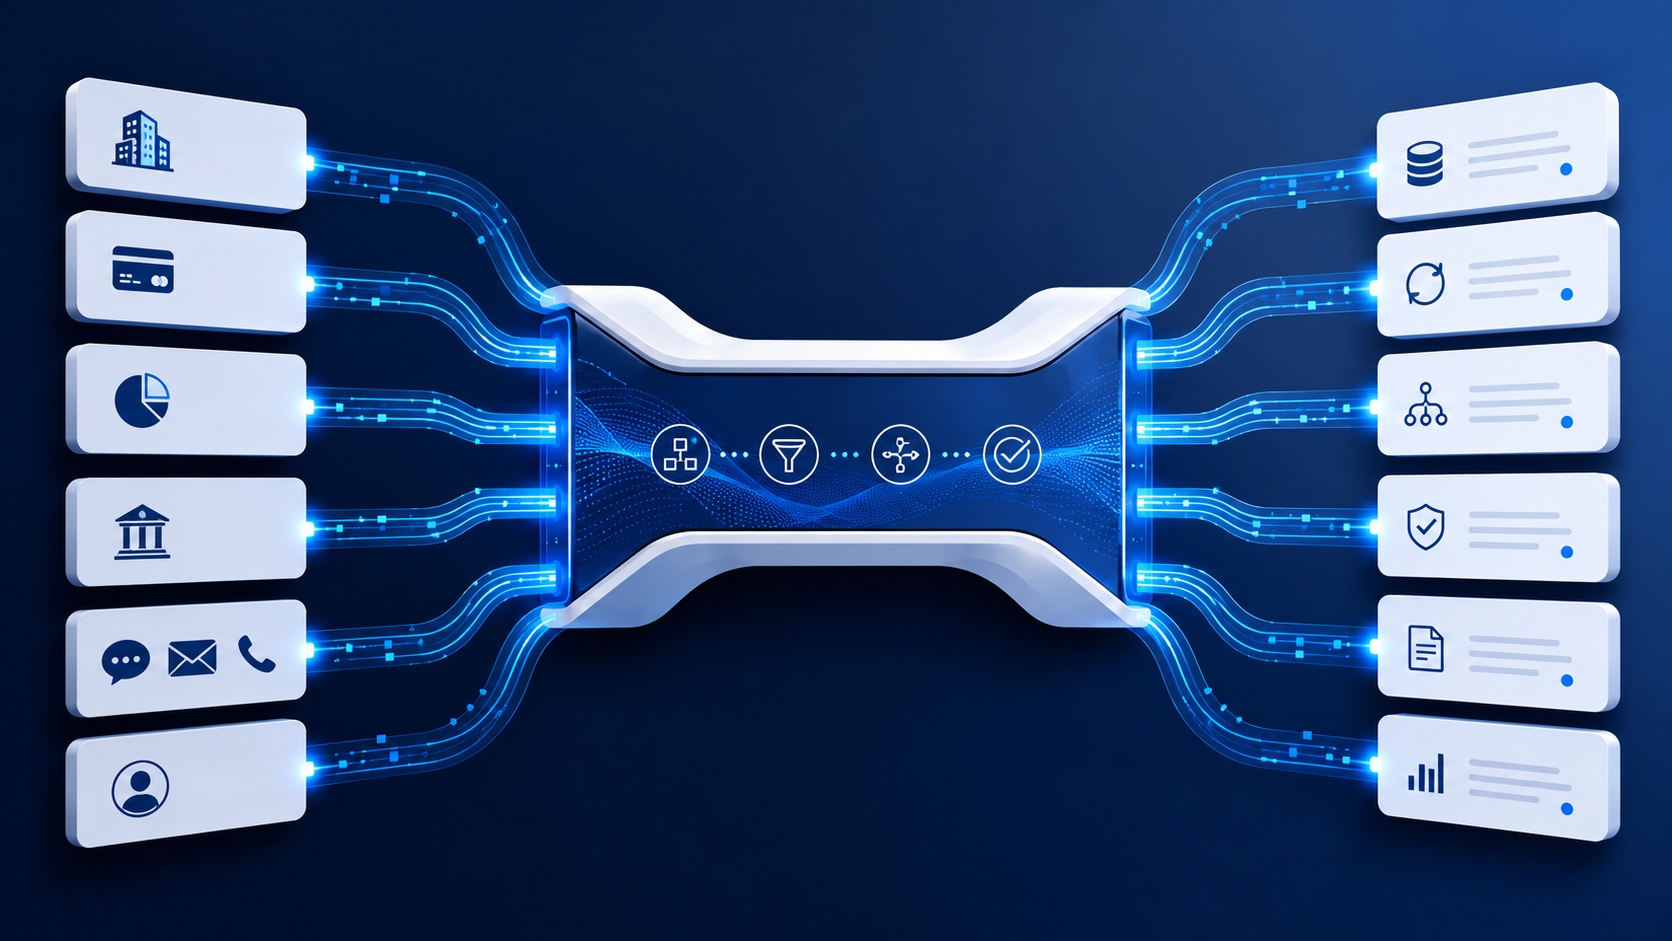
Healthcare debt collection software may exchange data with an EHR, revenue-cycle platform, accounting environment, payment provider, or reporting system. Depending on the agency, the broader technology stack may include ERP systems, payment and engagement tools, and other specialized collection platforms.
Placements, payments, returned accounts, documents, and status updates should move reliably between systems. API integration can provide faster synchronization, while batch exchange may still fit some workflows.
Strong debt collection software integrations should give enterprise agencies confidence in data accuracy, system connectivity, and how failures or exceptions are handled across the stack.
Validate Placement Data Before Accounts Enter Production
Bad data should become an exception before it becomes collector work. Validation rules can flag missing fields, invalid identifiers, duplicate accounts, incorrect balances, or missing documentation at intake.
Those issues can route into a data-quality exception queue. Queue management keeps the account out of normal production until the problem is resolved. Segmentation tools can then organize valid accounts by client, balance, service type, age, or other approved criteria. Predictive analytics, machine learning, and risk scoring may support prioritization when inputs are understood and human oversight remains available.
Build Auditability Around Every Data Change
Audit trails should answer four basic questions: who changed the record, what changed, when it changed, and what the original value was. That includes manual edits as well as automated updates from integrated systems.
Real-time dashboards can help managers monitor placement errors, exception volume, payment activity, and unresolved client issues. The point is to make data quality visible enough to manage. Stronger auditability can support client confidence, operational control, and more consistent debt management without making the platform healthcare-only.
Healthcare Software Evaluation Checklist
When evaluating healthcare debt collection software, examine the data model, permissions, EHR integrations, documents, audit trails, workflows, payments, reporting, self-service portals, and security controls. Test payment plans, online payment activity, disputes, recalls, and client-specific rules in real workflows.
Aktos fits this evaluation as modern debt collection software with configurable workflows, permissions, integrations, reporting, payments, and auditability. Healthcare is one portfolio type it can support, not the only market it serves.
Final Thoughts: HIPAA Is the Floor, Not the Data Model
A healthcare collection operation needs secure technology, but security alone does not create a workable account. The agency also needs accurate patient and guarantor data, service context, supporting documents, client rules, controlled access, and dependable system synchronization.
The strongest healthcare debt collection software makes those pieces work together so collectors can focus on resolution instead of reconstruction. That is where modern architecture can improve both operational consistency and the quality of the client relationship.
FAQs
Q: What should healthcare debt collection software include?
A: It should support secure account data, patient and guarantor relationships, service context, documents, client rules, payments, audit trails, role-based access, reporting, integrations, disputes, and exceptions.
Q: What healthcare data should creditors send collection agencies?
A: Agencies should receive authorized data needed to identify the account, understand the balance, support the debt, follow client rules, and communicate appropriately. Define the exact data set with the creditor and qualified counsel.
Q: How should collection software integrate with EHR systems?
A: The integration should use reliable identifiers, defined data ownership, validation, error handling, secure transmission, and clear rules for how placements, payments, documents, recalls, and status changes synchronize between systems.
Q: Is HIPAA compliance enough when evaluating collection software?
A: No. HIPAA considerations are important for applicable healthcare data, but buyers should also evaluate workflow design, data quality, integrations, access controls, reporting, payments, scalability, and the broader compliance requirements that apply to the agency.